

Deep packet inspection through User Defined Filtering (UDF) with Open Packet Broker
 April 8, 2024
 Deep Network Observability
Indeed, in enterprise environments where traditional network monitoring and filtering methods may not provide the desired level of accuracy or granularity, Deep Packet Inspection (DPI) can be a valuable solution. DPI goes a step further by analyzing the entire content of data packets. This allows for a more comprehensive understanding of the data being transmitted.
Why do we need Deep Packet Inspection?
Customization and Specific Offset Inspection: DPI can be tailored to meet the specific needs of the enterprise. Network administrators can define the offsets within data packets that they want to inspect. This level of customization enables precise filtering and monitoring based on the exact location and values within the packet.
Enhanced Accuracy: By focusing on specific offsets and values within data packets, DPI can provide enhanced accuracy in identifying and classifying traffic. This is particularly valuable when dealing with complex or non-standard protocols and applications.
Security and Threat Detection: DPI's ability to inspect specific offsets allows for the detection of specific patterns, signatures, or anomalies within data packets. This is instrumental in identifying and mitigating security threats, including advanced and zero-day attacks.
Custom Policy Enforcement: Enterprises can enforce custom policies based on the content found at specific offsets. For example, they can filter out sensitive data, block certain types of content, or prioritize specific applications or services.
Data Loss Prevention (DLP): DPI can be used for data loss prevention by monitoring data packets for sensitive information, such as proprietary company data, and preventing their unauthorized transmission.
How does User Defined Filtering work in Aviz OPB?
User Defined Filtering (UDF) as implemented in the Aviz Open Packet Broker (OPB) built over the open-source Software for Open Networking in the Cloud (SoNiC) is a powerful and customizable network packet processing solution. This combination allows network administrators to perform deep packet inspection and filtering based on specific offsets within data packets, offering fine-grained control and flexibility.
Key aspect of User Defined filter:
- High level of granularity: Users can specify precisely what they want to filter or monitor, whether it's blocking access to certain websites, prioritizing specific applications or services, or monitoring traffic for specific keywords or patterns.
- Use cases: UDF with deep packet inspection is valuable for various use cases, including security threat detection, application recognition, content filtering, and compliance enforcement. For example, administrators can use it to block malicious payloads, prioritize or de-prioritize specific application traffic, or enforce content policies.
- Flexibility and Adaptability: UDF in Aviz OPB provides flexibility and adaptability, allowing organizations to respond to evolving network conditions and security threats. Administrators can modify filtering rules as needed to address changing requirements.
- Monitoring and Reporting: Aviz OPB often includes monitoring and reporting capabilities. Administrators can monitor network activity, generate reports on traffic patterns, and gain insights into network behavior.
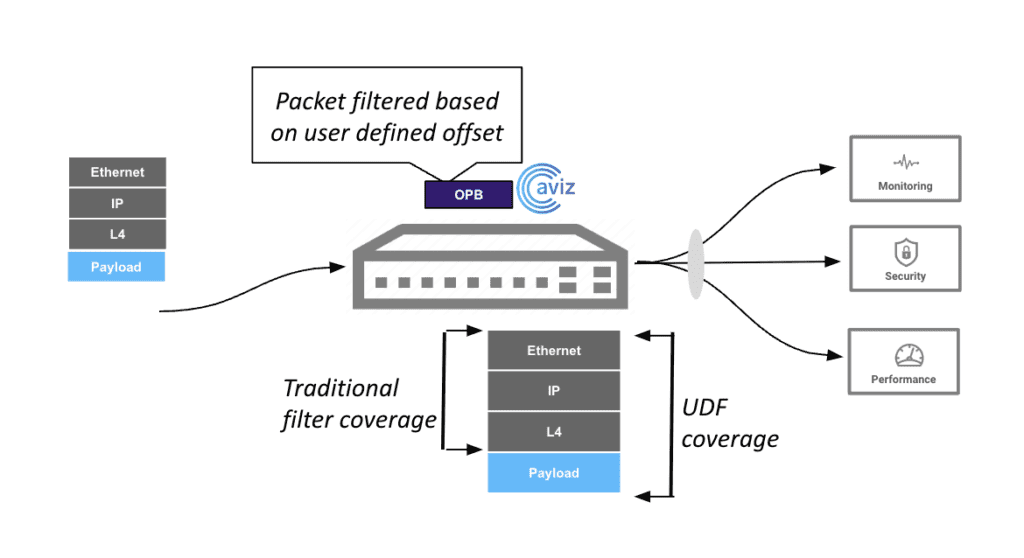
Using UDF, users can configure a rule to match specific bytes in the ingress packet based on a given offset to permit or deny matched packets:
- Offset for the L3 packet starts from the IP header in the packet
- Offset for the L2 packet starts from EtherType in the packet
flow flow1 network-ports Ethernet12/1 tool-ports Ethernet14/1 rule 1 permit description "UDF" udf-data 0xb166 udf-extraction-group l2 udf-offset 2 counters enable rule 2 permit description "UDF" udf-data 0x4500 udf-extraction-group l3 udf-extraction-point ipv4 udf-offset 0 counters enable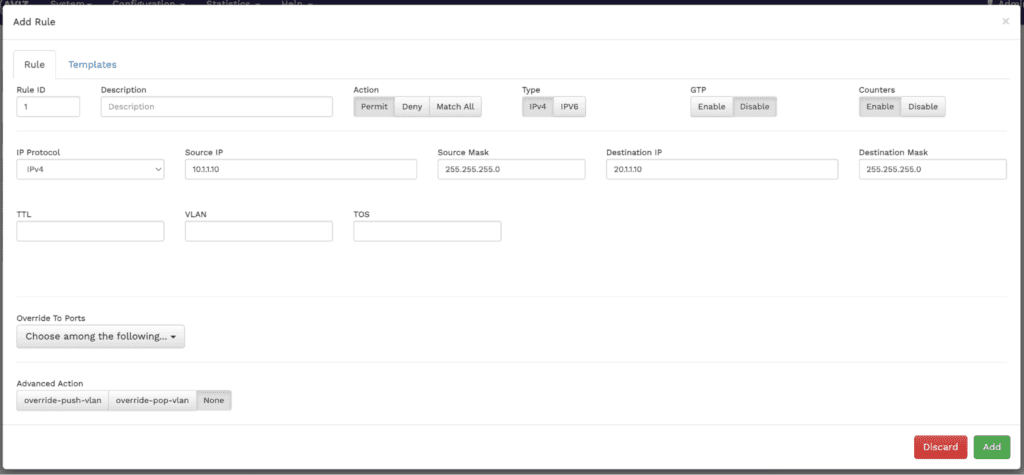
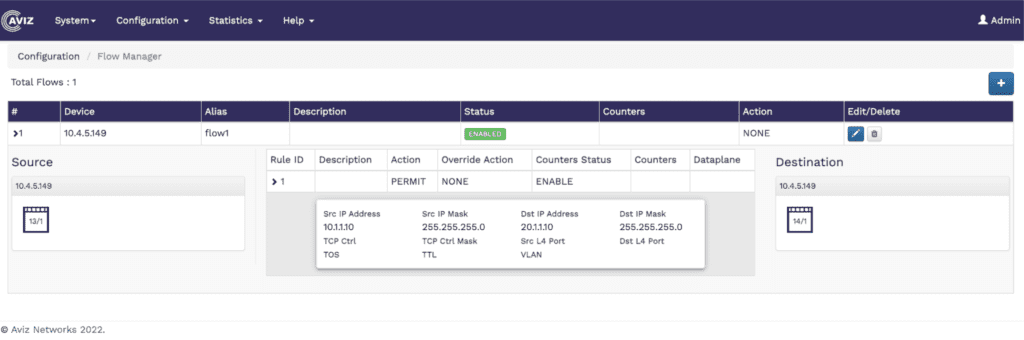
Aviz OPB and UDF: The Ultimate Solution for Precise Network Traffic Control
Overall, the combination of Aviz OPB and UDF offers advanced network packet processing capabilities with deep packet inspection and filtering based on specific offsets defined by network administrators. This level of customization is valuable for organizations that require precise control over their network traffic to meet security, compliance, and performance objectives with minimal cost using SONiC.
Ready to Experience the Power of Aviz OPB? Contact Us Today!
FAQs
1. What makes Aviz Open Packet Broker (OPB) different from traditional network packet brokers?
Aviz OPB, built over open-source SONiC, offers a cost-effective, highly customizable solution compared to traditional proprietary packet brokers. It enables fine-grained, offset-specific deep packet inspection (DPI) through User Defined Filtering (UDF), giving enterprises precise control over traffic without vendor lock-in or high licensing costs.
2. How does Deep Packet Inspection with UDF help in advanced threat detection?
DPI with UDF allows administrators to inspect specific byte offsets within packets, enabling detection of malicious patterns, signatures, or anomalies that may indicate zero-day attacks or advanced persistent threats.
3. Can Aviz OPB with UDF be used for compliance and data loss prevention (DLP)?
Yes, by monitoring packets for sensitive data at specific offsets, organizations can enforce compliance policies and prevent unauthorized transmission of proprietary information.
4. What types of network environments benefit most from using UDF and DPI with Aviz OPB?
Enterprises requiring precise traffic control, financial institutions, healthcare organizations, and any environment dealing with sensitive data or complex traffic patterns benefit most from UDF and DPI capabilities.
5. How easy is it to update or modify UDF rules in Aviz OPB as network requirements change?
UDF rules can be easily modified through CLI commands or APIs, allowing administrators to adapt filtering rules quickly as network conditions or security requirements evolve.


