

Scalable, Secure Service Edge for AI Factories
Secure Connectivity and Tenant Network Services at the AI Factory Edge
Aviz Service Gateway securely connects AI Factory tenants to the internet, clouds, shared services, and other data centers. Orchestrated by Aviz ONES, it combines BGP/EVPN routing, VRF/VXLAN termination, NAT, elastic IPs, and stateful L3/L4 policy in a software-defined service edge.
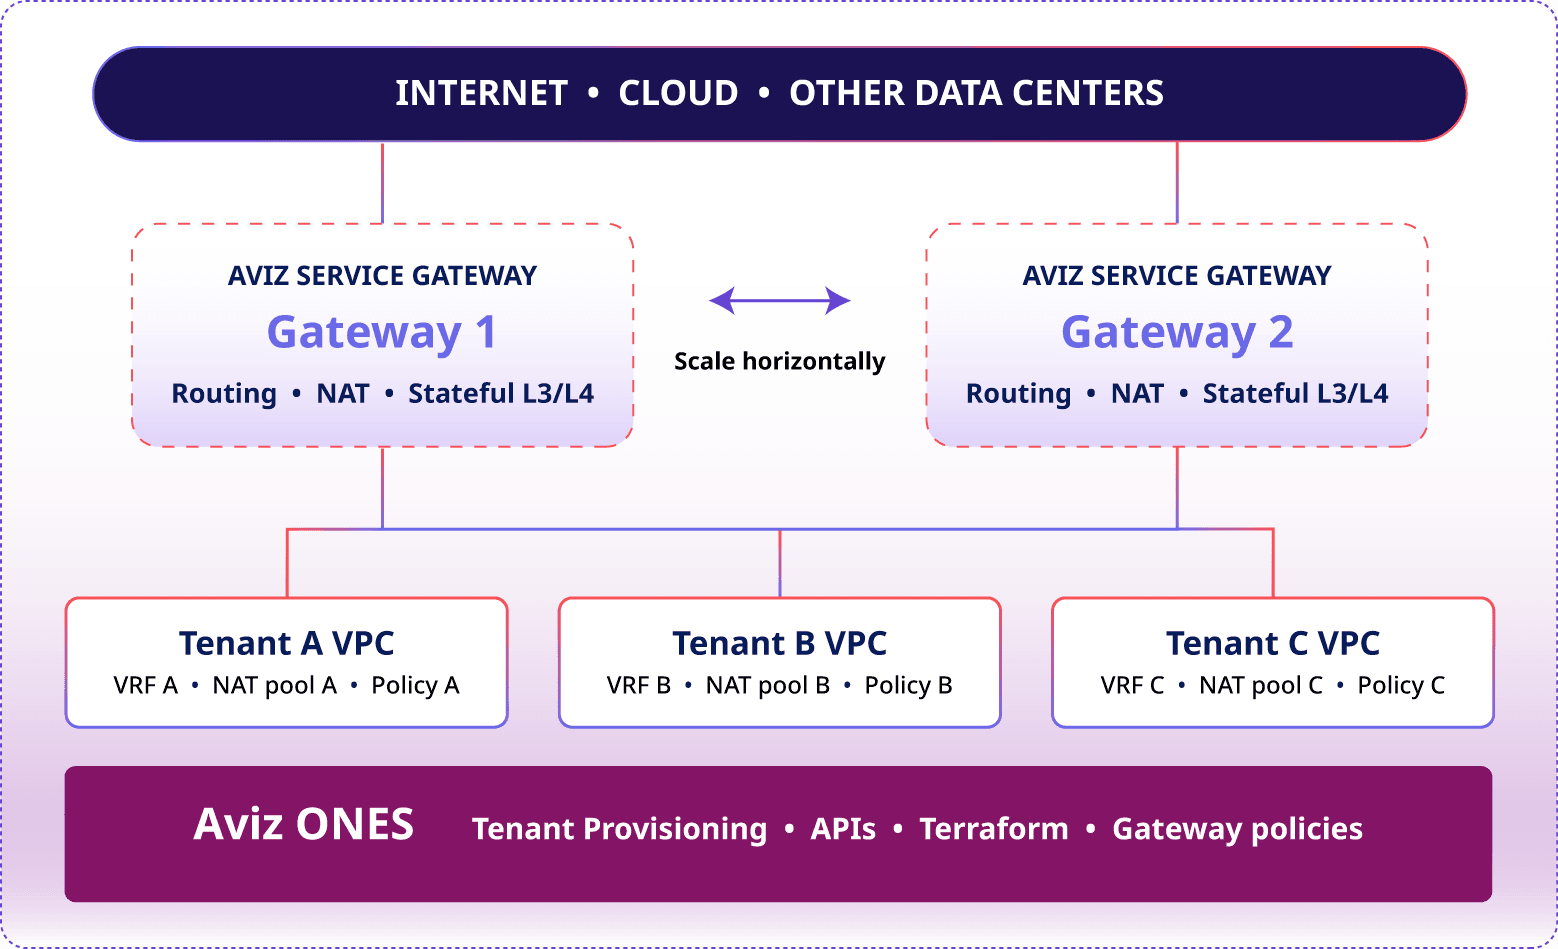
Control: Aviz ONES → gateway APIs/webhooks/Terraform. Data path: tenant traffic → gateway → external destination.
Scale tenant services
Horizontally add software gateway capacity instead of relying only on physical firewall appliance limits or switch ASIC VRF scale.
Preserve isolation
Separate VRFs, NAT pools, and session state keep tenants distinct even when private address ranges overlap.
Automate operations
Coordinate tenant connectivity and gateway services through ONES, APIs, and Terraform.
NAT & Elastic IP Services
Enable outbound Internet access and inbound application connectivity through tenant-aware NAT and elastic IPs.
Stateful Traffic Inspection
Track active connections and automatically permit legitimate return traffic while blocking unsolicited connections.
Shared services & storage
VPC peering and hub-and-spoke connectivity with intentional tenant boundaries.
Hybrid & multi-DC
Tenant-aware routing and security across AI Factory sites and clouds.
Tenant scale
Gateway VRFs and horizontal scaling support large multi-tenant infrastructure.
Policy Enforcement
Apply tenant-specific L3/L4 allow/deny rules based on IP addresses, protocols, and ports.
| Tier | NAT / FW sessions | CPU / RAM | NIC / throughput |
|---|---|---|---|
| Basic | 100K / 100K | 12 cores / 48 GB | 2×25G / 50 Gbps |
| Advanced | 250K / 250K | 16 cores / 64 GB | 100G / 100 Gbps |
| Performance | 500K / 500K | 32 cores / 128 GB | 2×100G / 200 Gbps |
Reference sizing from Aviz product brief; throughput and scale depend on configuration and workload.
