





3 AI Fears in Networking
 March 5, 2026
 Network Copilot ™
Network operations is entering a new phase: not just “AI for alerts,” but AI that can explain, recommend, and eventually execute workflows across your existing tooling.
That’s the upside. The reason many teams are still hesitant is also simple: the network is the business. When AI touches telemetry, configs, tickets, and change workflows, the fears are legitimate—and ignoring them is the fastest way to stall adoption.
Below are the three most common AI fears I see in networking.
Fear #1: “If I feed AI my network data, I’ll leak something sensitive.”
AI can deliver real productivity gains—but it also creates a new kind of visibility gap for IT and security teams.
The challenge isn’t just that employees might paste sensitive content into an AI chat window. It’s that AI traffic doesn’t behave like traditional enterprise application traffic:
- It’s frequently encrypted end-to-end
- It’s often API-driven (not a single, static app signature)
- It can move across data centers, edge locations, and hybrid clouds
- And it increasingly includes both sanctioned and unsanctioned (“shadow AI”) usage
That combination makes “who is sending what to which AI service” harder to answer with legacy monitoring approaches. Traditional DPI and monitoring methods that rely on ports, headers, or static signatures often can’t reliably identify or classify modern AI interactions—especially when they’re encrypted or routed through changing APIs.
1.1 Why “Shadow AI” becomes a data privacy problem
“Shadow AI” is any AI app or AI API being used outside approved IT controls—for example, an employee using an AI tool to speed up work without an approved workflow, policy, or governance.
That matters because it introduces privacy and compliance risks that are easy to underestimate:
- Data privacy leakage: source code, credentials, customer information, or strategic docs get uploaded to AI tools
- Compliance exposure: regulated data may leave controlled systems, breaking internal policies or contractual obligations
- IP loss: prompts and attachments can contain proprietary implementation details
- New attack paths: unmonitored AI interactions can become surfaces for prompt injection or manipulation attempts
In short, you can’t protect what you can’t see. And AI adoption can outpace visibility if organizations don’t modernize how they detect and govern AI traffic.
1.2 What “good” looks like: privacy-by-design visibility
A practical way to reduce privacy risk—without slowing adoption to a halt—is to aim for real-time, application-aware visibility into AI usage, including both sanctioned and shadow AI, across hybrid environments.
That typically means augmenting legacy monitoring with capabilities designed for today’s encrypted, API-driven patterns:
- Context-aware application identification that can distinguish AI services and usage patterns (not just ports/protocols)
- Payload-aware or metadata-enriched inspection to classify AI interactions accurately (within your organization’s policy constraints)
- Unified analytics and dashboards so security and network teams can see AI usage trends by app/user/site, and enforce policies consistently
1.3 How teams should start (low risk, high impact)
If you want an actionable starting point for Fear #1, here’s a simple progression:
- Define what’s allowed
List approved AI tools and the kinds of data that may (and may not) be shared. - Establish visibility first
Measure current AI usage, including shadow AI, across branches/remote/edge/cloud paths.
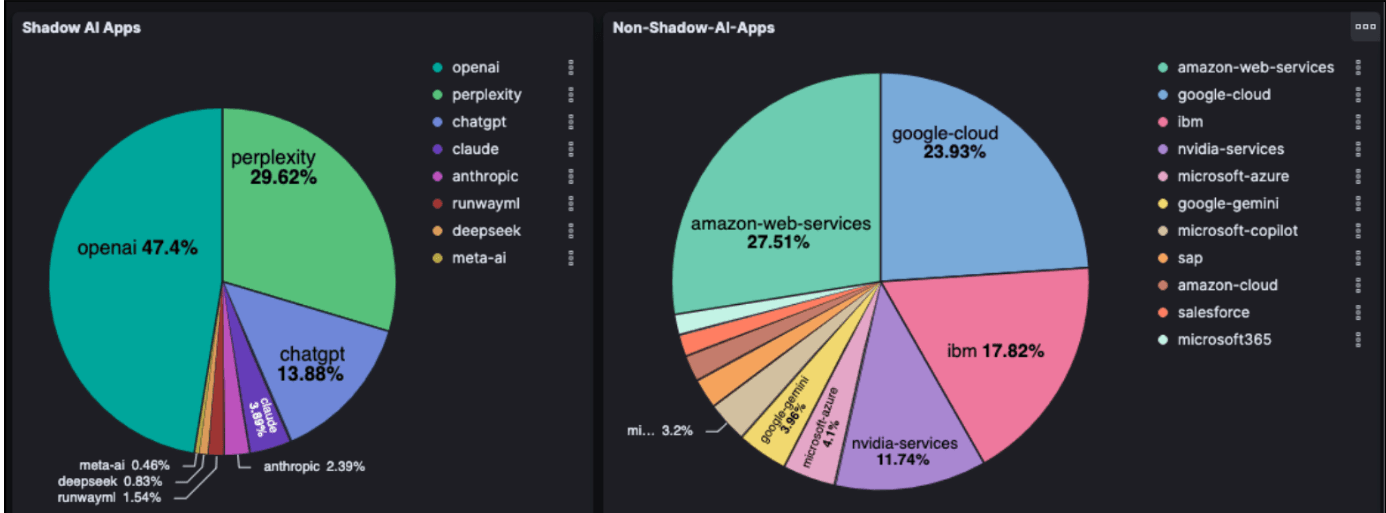
Figure 1: Shadow and Non-shadow AI Apps Identification using Aviz Elastic Node
- Classify and control data flows
Identify the highest-risk data types (customer data, credentials, source code, regulated data) and implement detection + policy enforcement for those flows. - Make it easy to do the right thing
Provide a sanctioned path (approved tools, guidance, redaction practices, training) so employees don’t route around IT.
This way, privacy governance becomes an enabler: teams can adopt AI with control, rather than pretending AI use isn’t happening until a leak forces attention.
Fear #2: “Our network is mission-critical. How do we trust AI without risking an outage?”
Fear #1 is about data leaving your control—and the reality that AI adoption can outpace visibility and governance. But even after you improve visibility and put privacy guardrails in place, a second fear shows up fast in networking:
2.1 What happens when AI is wrong, and the network is the business?
As mentioned in Deciding the Future: Building New Networks for the AI Era by Vishal Shukla, the safest way to adopt AI in operations is to treat it as a progression from ingest - reason - act, and to extract value early from ingest/reason before expanding into act.
2.2 Trust isn’t a switch —it’s a staged path to autonomy
Instead of debating “copilot vs agent,” the practical approach is a trust ladder: start bounded, prove reliability, then expand.
Stage 1 — AI that reads and explains (no production changes)
This is the lowest-risk way to create value, because you are not touching the control plane. You can validate outputs, measure impact, and build confidence without introducing outage risk.
Examples that fit mission-critical NetOps:
- Incident summarization and timeline reconstruction (telemetry + tickets)
- Correlation and hypothesis generation (“most likely causes” + why)
- Drafted troubleshooting workflows (“what should we check next?”)
Trust goal: faster, more consistent operator decisions—without autonomous change.
Stage 2 — AI that orchestrates low-risk workflows (guardrails + approvals)
Once visibility and privacy governance are in place (Fear #1) and Stage 1 proves useful, the next step is AI-driven workflow orchestration—still governed, still auditable.
As noted in the book, agents become operationally safe when they operate through controlled tool access with governance controls like approvals and auditability.
Good Stage 2 actions:
- Automated evidence gathering (read-only checks across tools)
- Pre-change validation runs
- Change-plan drafting + rollback-plan drafting for human approval
Trust goal: reduce toil and improve consistency while keeping humans accountable for high-impact actions.
Stage 3 — AI that acts (only inside a safety cage)
This is where mission-critical fear peaks—and where teams either do it right or get burned.
The key lesson is simple: weak guardrails create governance gaps.
So if you allow execution, constrain it:
- Maintenance window enforcement
- Tight blast radius (one device/site/domain)
- Mandatory rollback steps and success criteria
- Full audit trail (who/what/when/why)
- Clear decision on where AI runs (on-prem/private/public) based on risk tolerance
Trust goal: AI executes repeatable, bounded actions safely—never “free-running automation.”
2.3 How leaders should start (and why this connects back to Fear #1)
Fear #1 established the core principle: you can’t govern what you can’t see.
Fear #2 builds on it: you can’t trust what you can’t constrain.
A practical leader’s path looks like this:
- Make AI usage visible (including shadow AI) → reduces privacy risk
- Prove value in read-only + explain mode → builds trust safely
- Add orchestration with approvals + audit → reduces toil without outages
- Only then allow bounded execution → autonomy earned, not assumed
Fear 3: “Even if it works, I’ll lose control of governance, cost, and who’s doing what with AI.”
This is the “leadership” fear, and it’s showing up everywhere—not just in networking.
On the personal side, Gartner’s Peer Community research found that 90% of CIO respondents expressed some concern about the potential loss of control over AI systems, with half describing their worry as only slight.
In other words: leaders aren’t universally panicking—but they’re not ignoring the risk either.
On the operational side, loss of control shows up as:
- Teams using unapproved AI tools (privacy + compliance risk)
- AI-driven changes without clear accountability
- Tool sprawl and duplicated “AI features” across the stack
- Costs scale unpredictably as usage grows
Cost is a particularly sharp edge: Gartner data reported by CIO.com found 90% of CIOs cite out-of-control costs as a major barrier to achieving AI success, and warned that without understanding scaling dynamics, companies can dramatically underestimate costs.
3.1 How to stay in control: governance that accelerates, not blocks
1) Assign an accountable owner
Gartner’s guidance on AI-era data governance explicitly calls out the need to appoint an AI governance leader and build cross-functional collaboration across cybersecurity and data stakeholders.
2) Establish “lighthouse principles” for AI in NetOps
Gartner’s CIO guidance on becoming “AI-ready” stresses that organizations need principles that define what kinds of human-machine relationships they will and won’t accept—and notes that few organizations even have an AI vision statement in place.
For networking, lighthouse principles can be as concrete as:
- “AI can recommend any change, but cannot execute L3/L4 policy changes without approval.”
- “All AI actions must be replayable and reversible.”
- “No production secrets or customer identifiers may be submitted to public GenAI.”
3) Create an operating model for agents
If you move beyond chat into agents, define:
- Who authors agent workflows?
- Who approves them?
- Who owns the runbook when it fails?
- How often are workflows reviewed?
- What’s the deprecation process?
4) Build cost controls into the design
Don’t treat cost as “later.” Treat it as a non-functional requirement:
- Usage quotas per team/use case
- Cost dashboards (by use case, by workflow, by team)
- Architecture choices that reduce repeated calls (caching, retrieval optimization)
- PoCs that test cost scaling, not just technical feasibility
3.2 The leadership angle: Integrating AI is now part of the job
Whether your title is CIO, VP Infrastructure, Head of NetOps, or Network Architect: AI adoption is no longer a side project. Gartner has explicitly positioned GenAI as an enterprise initiative and urged leaders to decide their AI ambition and become AI-ready.
And leadership expectations are rising: one summary citing Gartner’s 2024 CIO GenAI survey notes that 48% of CIOs report being the single executive responsible for AI efforts.
In networking terms, that means leaders should be ready to answer:
- What network workflows will AI touch first—and why?
- What data is allowed to be used, where, and under what controls?
- What’s our trust model (copilot vs agent)?
- How do we prevent shadow AI while still enabling productivity?
- How will we measure value (time saved, incidents prevented, risk reduced)?
3.3 Closing thought
AI in networking will create both momentum and skepticism—and that’s the correct instinct when the network is the business. The goal isn’t to “believe in AI.” It’s to engineer trust the same way we engineer reliability: with visibility, guardrails, and accountability.
If you take only one thing from these three fears, let it be this: each fear maps to a concrete requirement you can build into your rollout.
- Fear #1 (Privacy): If you can’t see AI usage—sanctioned and shadow—you can’t govern it. Start with visibility, data boundaries, and policies that make the safe path the easy path.
- Fear #2 (Mission-critical trust): Don’t jump to autonomy. Earn it. Begin with AI that reads and explains, then orchestrates low-risk workflows, and only then acts—inside a safety cage with approvals, rollback, and blast-radius limits.
- Fear #3 (Loss of control): Treat AI as an operating model change. Assign an owner, define lighthouse principles, design for auditability, and manage cost like a first-class constraint.
The leaders who will win this transition won’t be the ones who move fastest or the ones who block hardest. They’ll be the ones who move deliberately: start small, prove value, measure outcomes, and expand responsibility to AI only when the system is observable and governed.
Because in networking, “AI-ready” doesn’t mean “more automation.” It means automation you can explain, constrain, and trust.
Frequently Asked Questions
1. Why are network teams cautious about using AI in operations?
Because AI touches sensitive areas like telemetry, configurations, tickets, and change workflows, any mistake can directly impact the business. The network is mission-critical, so trust and governance matter more than speed.
2. Why does AI usage increase data privacy risk in networks?
AI traffic is encrypted, API-driven, and spans data centers, edge, and hybrid clouds. Traditional monitoring tools struggle to identify who is sending what data to which AI service.
3. What is shadow AI and why is it risky?
Shadow AI refers to AI tools or APIs used outside approved IT controls. It increases the risk of data leakage, compliance violations, IP loss, and unmonitored attack paths.
4. Why is visibility the first requirement for AI governance?
Without visibility into sanctioned and shadow AI usage, organizations cannot enforce privacy policies or data boundaries. You cannot govern or protect AI usage you cannot see.
5. What does privacy-by-design visibility for AI look like?
It includes real-time, application-aware identification of AI services, enriched metadata inspection, and unified dashboards showing AI usage trends by user, app, and site.
6. Why do teams worry about AI causing network outages?
If AI makes incorrect decisions in a mission-critical network, the impact can be immediate and severe. This makes unrestricted AI-driven execution risky without safeguards.
7. How should AI be introduced safely into network operations?
AI adoption should follow a staged model: start with read-only explanations, then orchestrate low-risk workflows with approvals, and only allow execution inside strict guardrails.
8. What types of AI actions are safe in early adoption stages?
Safe early actions include incident summarization, telemetry correlation, hypothesis generation, evidence gathering, and drafting troubleshooting or change plans without execution.
9. Why is governance a major leadership concern with AI?
Leaders worry about losing control over who uses AI, how decisions are made, and how costs scale. Unapproved tools, unclear accountability, and unpredictable spend increase risk.
10. How can leaders stay in control while adopting AI?
By assigning clear ownership, defining lighthouse principles, enforcing auditability, and building cost controls into AI design. Trust is engineered through visibility, constraints, and accountability.


